








GCSA Insights: Binance Approximately 6.3 Billion USD Theft Incident Independent Forensics and EIP-7702 Attack Link Analysis
 Core Viewpoint


 How do attackers bypass the security boundary between internal enterprise systems and on-chain wallets, converting certain access permissions into the ability to transfer assets effectively?
Author: AI and Cybersecurity GCSA
Preface
Billions of dollars in digital assets have been transferred, yet the wallet private keys have not been confirmed as leaked. This is the most pressing contradiction in the Binance security incident: how did the attackers bypass the security boundary between the internal systems and on-chain wallets, converting some form of access permission into the ability to transfer assets effectively?
According to Binance's preliminary disclosure, the incident may have begun with the compromise of a DevOps engineer's laptop, subsequently affecting internal service containers and unauthorized withdrawal processes. Meanwhile, TRM Labs has attributed the incident with high confidence to North Korean-related threat activity TraderTraitor; on-chain investigators have also raised suspicions related to Lazarus. These judgments provide context for the incident but do not replace the technical verification of each key transaction, nor can they directly prove the identity of the actual operators.
GCSA's special evidence collection chose a different entry point: not focusing on the total loss or attributing it to the attackers as an endpoint, but rather returning to publicly verifiable transactions, signatures, and states. The study reviewed 18 original transactions and their outer signatures, verified 50 initial authorization signatures and 1 revocation authorization signature related to Binance 14, and tracked delegated calls, asset transfers, zero address revocations, and the designated block states of frozen wallets.
Among them, a type-4 transaction contained 50 authorizations, but this does not equate to 50 delegated actions being effectively executed; valid signatures prove signing capability but do not infer whether the private key was stolen or which internal system initiated the request. GCSA further verified three consecutive transactions associated with MetaMask Gas Station: the deposited ETH precisely matched the maximum Gas budget of the subsequent two transactions, providing a verifiable basis for analyzing third-party service interactions. However, the claims that "the attacker mistakenly selected USDT," that MetaMask holds the real IP, and that identity is locked by IP are currently just unverified speculations.
This is also the main difference between this report and general incident reports: clearly separating "observed on-chain facts," "evidence-based technical inferences," and "root causes and identity attribution that still require off-chain evidence collection." The review of key Ethereum links is not a full audit of ten chains; being blacklisted does not equate to having recovered the assets; the estimated impact of approximately $6.3 billion cannot be directly viewed as the final net loss.
The implications of this incident extend beyond a single exchange. The boundaries of digital asset security have long since expanded from the private key itself to terminal devices, signing services, permission approvals, continuous delivery environments, and third-party infrastructure. Public ledgers can restore how assets move, but to truly answer "how permissions were compromised and who operated behind the scenes," a complete chain of on-chain and off-chain evidence is still required.
GCSA Key Findings
Authorization Mechanism: All 50 EIP-7702 signatures were verified as valid signatures for the corresponding wallets, but the validity of the signatures and the actual execution of the authorizations are two separate issues and cannot directly conclude that the private key has not been leaked.
Funding Path: The report verified part of the Ethereum asset transfers of Binance 14 and Hot Wallet 34; the coverage is focused on key transaction samples, not an independent write-off of total cross-chain losses.
Gas Station: The associated recharge amount precisely matches the maximum Gas budget of the two transactions. This may indicate subsequent legal preservation of service logs, but does not represent that IP has been obtained or real identity confirmed.
Disposal Status: The report verified delegated revocations, USDT blacklists, and target wallet balances; revoking authorization, freezing assets, and actual returns are different evidentiary matters.
Research Scope: This independent review focuses on key Ethereum transactions. The root cause of the intrusion, full cross-chain write-off, actual recovered amounts, and the identity of the attackers still require further evidence support.
Special Evidence Collection Report
GCSA Binance Network Attack Special Evidence Collection Report
October 30, 2026 | Full Event Review and Key Ethereum Link Verification | Version 2.0
Data retrieval cutoff: 2026-10-30 14:03 JST (Japan, UTC+9) / 2026-10-30 05:03 UTC.
On-chain status anchor point: Block 26303316, 2026-10-30 04:55:47 UTC. This report is an updated snapshot as of the above time point.
Core Conclusion
Official disclosures and cross-chain investigation materials have formed a platform-level security incident. Key on-chain evidence supports the EIP-7702 delegation, asset transfers, and subsequent zero address revocations of Binance 14; the complete root cause of the intrusion, final net loss, and actual recovered amounts remain unresolved.
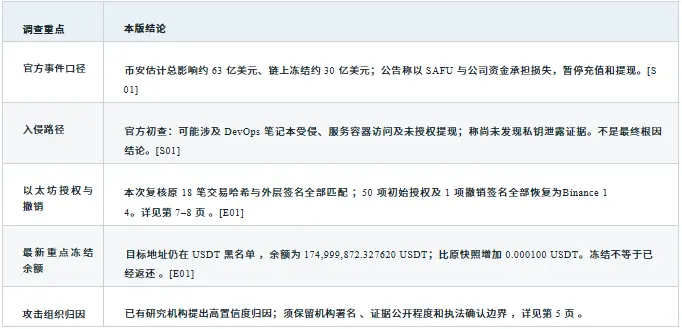
Report Scope and Reading Navigation
Maintaining the original report structure of "Evidence Method, Address, Authorization, Revocation, Gas Station, Fund Flow, Path Map, Transaction Index, Unresolved Evidence," new additions include the full event timeline, amount criteria, business impact, and disposal progress. The original template identifiers are used solely for document continuity and do not represent that this update has received separate endorsement from the institution.
Pages 2-5: Methods, Timeline, Total Amount and Attribution; Pages 6-11: On-chain Special; Pages 12-13: Impact and Subsequent Verification; Pages 14-15: Original 18 Transactions and New Transaction Index; Pages 16-17: Sources and Attachments.
Evidence Method and This Version Update
Source Level Identification: E = Public on-chain query this time; S = External public sources; O = User-provided original report
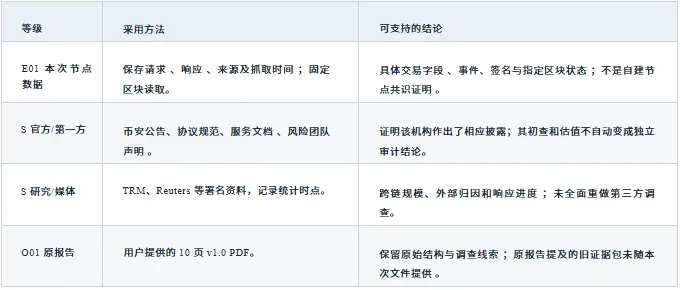
Substantial Updates Compared to v1.0
Added overall platform and cross-chain perspectives; separated official preliminary investigations from on-chain facts; re-encoded and verified the original 18 transaction hashes, outer signatures, and 51 authorization signatures; updated key USDT status anchor point to 26303316 and supplemented newly discovered micro transactions T19. Original numbering remains unchanged for easy reference.
Current Limitations and Irreplaceable Evidence
The two domains of PublicNode belong to the same provider and cannot be considered two independent node sources; another provider's access failed. Some queries for historical code and historical balances returned HTTP 403, thus failing to complete the replay of states before and after revocation or independent EVM instruction execution. Failed responses are also retained.
Some web pages are directly restricted from opening, and the text is read through indexed pages of search services; when the original post has access restrictions, only quoted media is used. The report distinguishes between the time of the incident, the time of report publication, the time of query, and the on-chain block time. If the announcement does not specify a time zone, no forced conversion is made.
This time, there was no access to internal terminals, HSM/MPC, approval systems, customer accounts, or law enforcement materials. No signatures or broadcast transactions were made, and no asset transfers, revocations, or external evidence requests were triggered. Any conclusions regarding the causes of internal systems and the identities of individuals cannot be determined solely from this public query.
Full Event Timeline
On-chain precise timestamps are primarily in UTC; JST = UTC+9, Beijing/Hong Kong time = UTC+8.
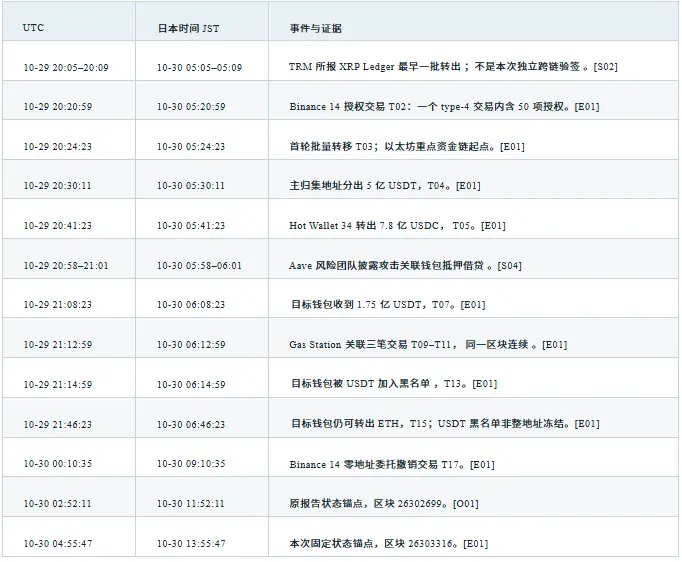
The Binance security announcement page shows 2026-10-30 02:23, but the page's time zone is not clearly stated, and no absolute timeline is inserted. One cannot confuse the first known transaction on a certain chain, the first media report, or the announcement publication time with the start time of the entire case's intrusion.
Loss, Freezing, and Recovery Criteria
The main table retains the original criteria from various sources; all amounts in USD refer to US dollars.
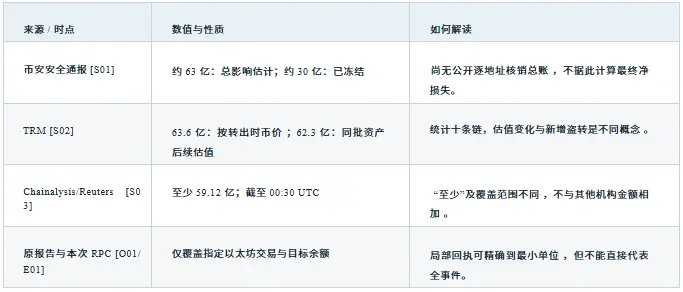
Cross-chain Scope and Current Investigation Coverage
TRM lists the scope as Ethereum, Bitcoin, Tron, XRP Ledger, Solana, Arbitrum, Optimism, Base, Avalanche, Polygon. Its key observation is that multi-chain ordinary signature transfers run parallel to Ethereum's delegation mechanism; this report's independent review focuses on Ethereum and does not claim to have completed the verification of each transaction on the other nine chains. [S02 / E01]
Freezing Parties and Disposal Criteria
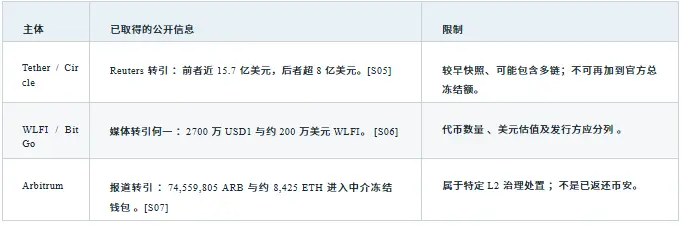
"Freezing" indicates that asset movement is restricted; "recovery" requires verifiable return or legal takeover; "compensation" requires evidence of deposit or payment. The arithmetic difference of 6.3 billion - 3 billion = 3.3 billion can only be considered an arithmetic difference between two approximations and cannot be deemed the final net loss, compensation gap, or what the attacker currently holds.
Intrusion Path and Attribution of Attack Organizations
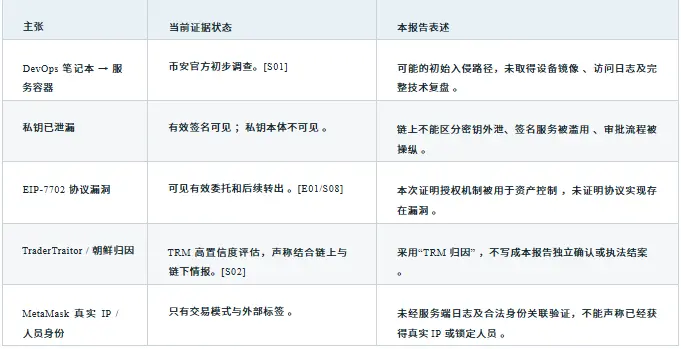
Separate on-chain capabilities, internal root causes, institutional attributions, and judicial determinations.
Currently Most Supported Technical Narrative by Evidence
There are valid delegated signatures for Binance 14, and the submitter placed these signatures into a type-4 transaction. Subsequently, external calls were executed in the context of the delegated account, resulting in bulk asset transfers. On-chain explains "what happened"; how signatures were generated, who controlled which devices, and how the approval system failed still require off-chain evidence.
A bulk nonce window may be used to adapt to high-frequency trading accounts; this is a mechanism explanation and cannot solely derive from the 50 authorizations that "the attacker does not have the private key" or "can only access the signing interface." Similarly, the official "no evidence of leakage found" does not equate to proving that all keys have never been exposed.
Causal Chain Still Needs Closure
Evidence of terminal compromise → Identity and session acquisition → Service container access → Business request/approval → Actual signature records → On-chain transactions. It must be linked with request IDs, signature hashes, time synchronization, and immutable logs; one transaction hash cannot replace the entire internal attack path.
Core Addresses
Address names follow the original report and block explorer labels; labels are not attribution fields in blockchain consensus.
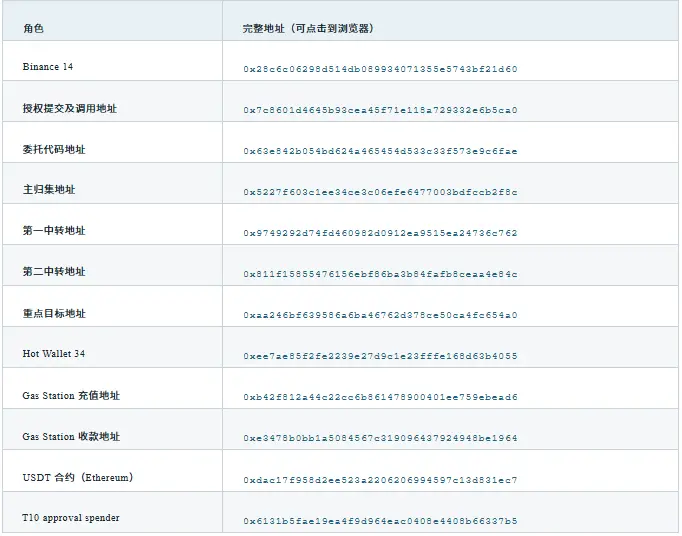
Transaction relationships can prove what actions occurred between addresses; one cannot determine the same controller, joint crime, or service provider responsibility solely based on receipt, fee payment, address tags, public service associations, or dust transfers. [O01/E01]
50 Authorized Itemized Verifications
Corresponding to T02; retain the original order of the authorizationList, do not replace the on-chain original order with the browser's sorting.
T02 is located at block 26300753, index 138; the time is 2026-10-29 20:20:59 UTC. Sender 0x7c86…5ca0, receiver Binance 14, outer nonce=10, input=0x, receipt successful. [E01]
This is 50 authorizations in a single type-4 transaction, not 50 separate authorization transactions. All chain_id are 1, and the delegate is 0x63e8…6fae; nonce ranges from 18,914,824 down to 18,914,775.
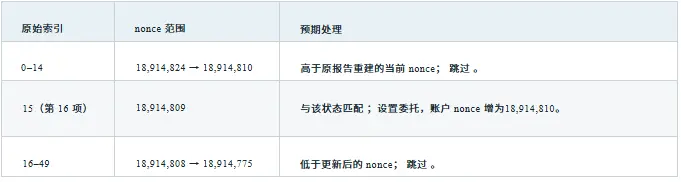
The T01 with the same block index 133 uses Binance 14 nonce 18,914,808. The original report reconstructs the nonce before authorization based on this and cross-verifies with browser validity records. This time, the entire block and authorization fields were retrieved, but there is no independent historical stateDiff/trace, so "Item 16 becomes effective" must retain this method boundary. [O01/E01]
Signature and Execution Validity are Two Types of Checks
All 50 initial authorization signatures have been restored to Binance 14; the 1 authorization for the revoked transaction also matches. Signature restoration checks whether it is effectively signed by the corresponding key; execution validity also relies on the nonce, code, and chain ID at that time. 50 valid signatures do not mean all 50 were executed. Attachments retain itemized results in original order. [E01]
The authorization summary is calculated by keccak256(0x05 || RLP(chain_id, delegate, nonce)). The protocol places authorization processing before execution; outer execution failures do not automatically revoke already effective delegations, so one cannot solely use receipt.status to determine whether the authorization is valid. [S08]
Revocation and Delegation Call at 00:10
Corresponding to T17; revoking delegation and reclaiming funds, revoking ERC-20 allowance are different operations.
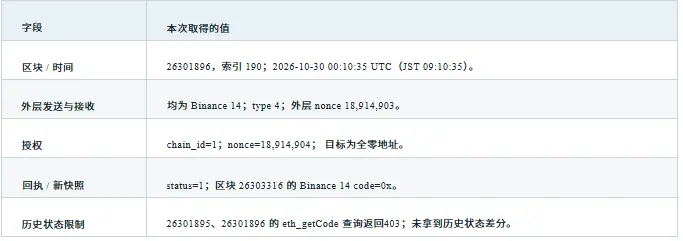
The outer nonce differs from the authorization nonce by 1, consistent with the processing order where the sender's nonce increments first. Authorizing a zero address means clearing the delegation code. The transaction content, protocol rules, and subsequent empty code support the revocation conclusion, but it cannot be described as independently replaying the execution state before and after the revocation. [E01/S08]
Risk Boundaries After Revocation
There is a gap of 3 hours, 49 minutes, and 36 seconds from T02 to T17. After clearing the delegation, subsequent calls no longer run the original code through that delegation; it will not retract already transferred assets, does not clear all ERC-20 historical allowances, nor can it prove that the original signature infrastructure has been repaired.
Delegation Contract Calls and Source Code Credibility
The original report records the first round selector 0x8a179be4, 65 entries in calldata (including ETH placeholder) and 64 receipt logs. Another call selector 0x043ff9d2 in T05 involves Hot Wallet 34, and the receipt supports its transfer of 780,000,000 USDC to the main aggregation address. [O01/E01]
The original report indicates that the browser Target.sol is an AI reconstruction display from 2026-10-30 00:30 UTC, not the attacker's original source code. Without obtaining independent compilation matching and per-instruction trace, one cannot determine its completeness as equivalent to deployment logic solely based on the source code page label. [O01]
MetaMaskGasStation Key Transactions
Block 26301011, 2026-10-29 21:12:59 UTC; T09--T11 are consecutively located at indexes 85, 86, 87.
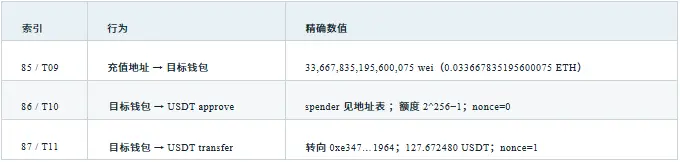
Maximum Gas Budget Verification
T10: 49,285 × 357,379,522,580 wei; T11: 46,503 × 345,233,327,425 wei. The sum of the two is 33,667,835,195,600,075 wei, which is precisely consistent with T09 recharge. [E01]
This verifies the upper limit of gasLimit × maxFeePerGas. This time, the actual costs for T10 and T11 calculated by gasUsed × effectiveGasPrice total 0.023108419450134449 ETH; it cannot be mixed with the maximum budget, nor can it infer exchange transactions based on ETH limits and USDT payment amounts. [E01]
Facts, Strong Inferences, and Unproven Matters
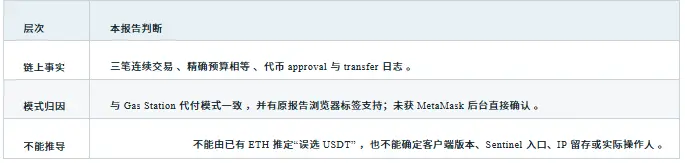
T08 shows the target wallet received 2 ETH at 21:10:59 UTC. MetaMask's official documentation states that when there are native tokens, other tokens can also be chosen to pay fees, so "already having ETH" and "using payment" are not contradictory. [E01/S09]
Fields available for subsequent legal associations include bundle, request ID, quotes, time, server access logs, and proxy chains. This is a suggestion for evidence preservation and does not indicate that any private logs have been obtained.
Fund Flow and Latest Freezing Status
The following are key links for Ethereum USDT; transfers are not counted repeatedly in the total event loss.
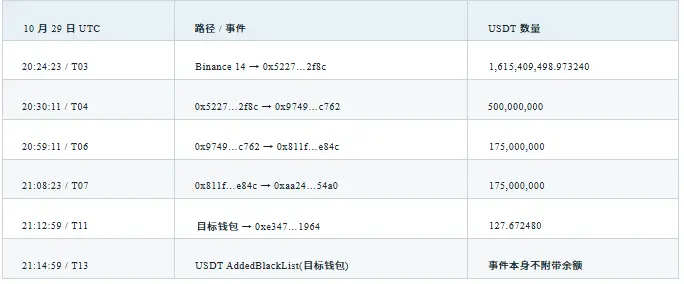
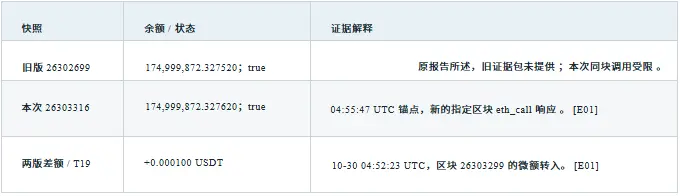
The original snapshot satisfies 175,000,000−127.672480=174,999,872.327520. The token sending address for T19 is 0xe347a7aa40f814469279760735c289cbcdbe1964, which is only similar at the beginning and end to the Gas Station receiving address, and the complete address is different. It should not be mistakenly recorded as the service provider making another payment or the attacker jointly controlling the address.
The incremental query range is from block 26302700 to 26303316, obtaining this transfer in, but no USDT out logs were returned to the target address. This window query is consistent with the new snapshot but does not equal the re-obtained old block balance.
20 ETH was received after T14; T15 transferred back 21.995031755405165251 ETH. The USDT blacklist does not freeze ETH or the entire Ethereum address. The second approve in T12 does not equal the completion of the exchange.
The first round of 167,464.247856558836135296 ETH comes from the original report's browser internal call display, and this time there is no trace, so it does not change the label to this independent execution evidence. The 780 million USDC in T05 and the approximately 823 million total reported externally are different coverage scopes.
Attack Path and Evidence Boundaries
Blue: On-chain links; Green: Disposal/Status; Yellow: Off-chain preliminary investigations or unresolved matters.
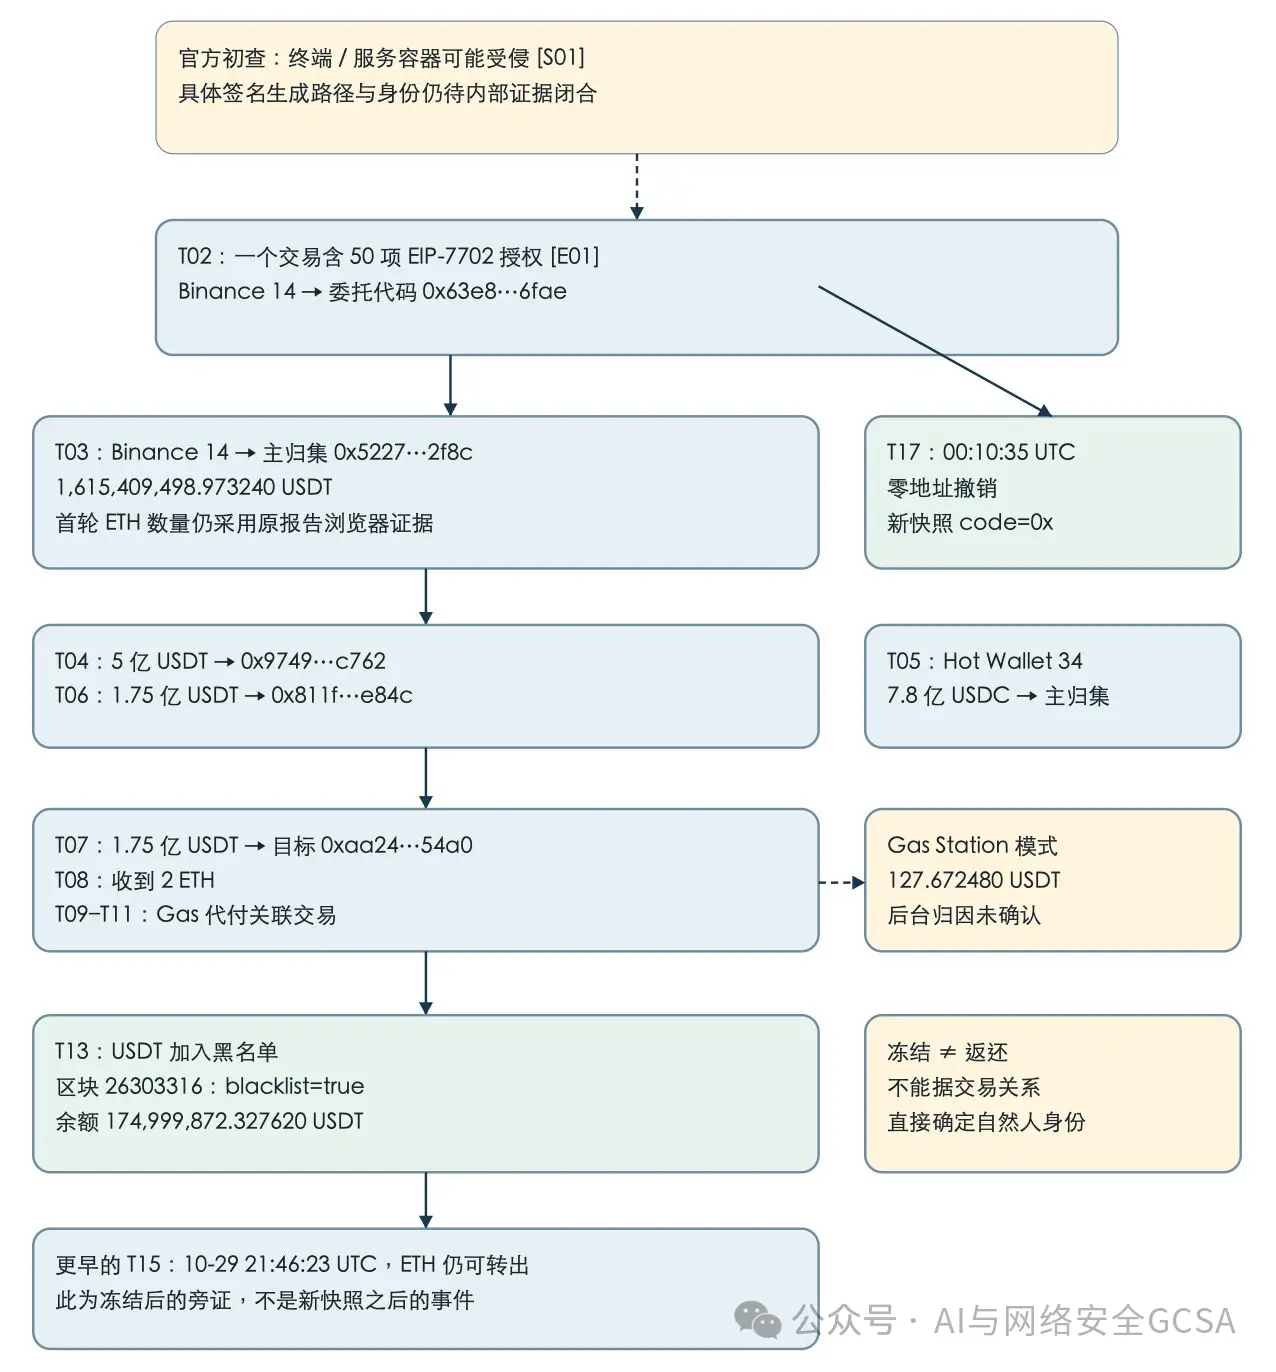
The main trunk in the figure only covers key Ethereum links. The cross-chain overview comes from signed research and does not expand this figure into a complete fund flow diagram of ten chains. The dashed line indicates associations that require off-chain evidence to be completed.
Business Impact and Ecological Disposal
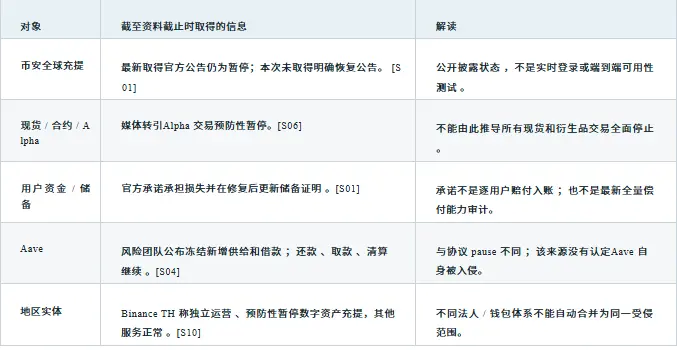
Records are made according to services, asset control, and user commitments; do not treat news headlines as the operational status of the entire platform.
DeFi Transmission Risks
LlamaRisk disclosed that the attack-associated wallet borrowed about 19,762 WETH with 60 million USDT collateral; its position disclosed at 01:00 UTC is still over-collateralized. Newly frozen positions are used to limit further borrowing, but existing utilization rates, collateral prices, and liquidation risks still need continuous observation. [S04]
Market Impact Should Be Treated as Event Point Data
Reuters reported that BTC and ETH fell during the event, and other studies estimated valuations changed with price fluctuations. This report does not attribute all market fluctuations after the event to the attack, does not package historical intraday prices as real-time quotes at the time of report delivery, nor does it provide trading directions based on this. [S03]
Current Actionable User Communication Guidelines
Recharge, withdrawal, and compensation arrangements are subject to new announcements from official channels; old wallets and attack addresses in the report are only for identification and verification. Any external messages claiming "unfreeze verification," "compensation collection," requiring wallet connections, mnemonic phrases, or transfers do not belong to the processing procedures verified by this report.
Unresolved Evidence
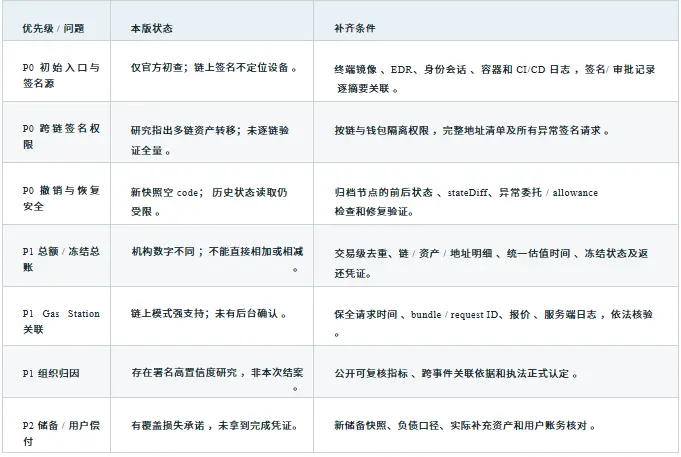
The following are work priority suggestions for subsequent verifications, which do not indicate that internal disposal, asset freezing, or contact with service providers has been executed.
Clear Update Trigger Conditions for the Next Version of the Report
Release official technical review or deposit and withdrawal recovery announcement; changes in frozen/returned status; obtain the total ledger for full-chain deduplication; appearance of verifiable new attribution evidence; or changes in the code, balance, or blacklist status of key addresses. Each update must retain the previous snapshot rather than overwrite historical values.
This report is a one-time cutoff snapshot. No background monitoring or automatic update tasks have been created; subsequent new changes will not be automatically written back to the delivered PDF.
Transaction Index
Complete hash can be viewed by clicking Etherscan; transaction numbers remain consistent with the original report. All RPC receipts this time are successful.
T01 Authorization before Binance 14 regular transactions
UTC 10-29 20:20:59 | Block 26300753 | Index 133 | Status 0x1
0xca63641eaeb49779d80ba11ce4fe894d635f2e98c032e9efd5bb4ce304ae56da
T0250 Item Delegation Authorization
UTC 10-29 20:20:59 | Block 26300753 | Index 138 | Status 0x1
0xad99264d5532ae0dd04b2004eebda05f25657e70dacb764f7ac8d4ccd051298b
T03 First Round Bulk Transfer
UTC 10-29 20:24:23 | Block 26300770 | Index 189 | Status 0x1
0x53bd38b816c23e74134786c29a8c18d792777998a3b9326047b583100e88e2f3
T04 Aggregation Address Diversion of 500 Million USDT
UTC 10-29 20:30:11 | Block 26300799 | Index 218 | Status 0x1
0x68d7d69deaeb9750c38020b4f8d3728146ca8d2267eba1e38cf9b56722ad659a
T05 USDC Transfer from HotWallet34
UTC 10-29 20:41:23 | Block 26300855 | Index 26 | Status 0x1
0xdc102dd89dded5a83f1008906883ffb7c81ff3b7d7965d8c7277d170b5e17481
T06 Transfer of 175 Million USDT
UTC 10-29 20:59:11 | Block 26300942 | Index 117 | Status 0x1
0x1fb992f92a45afec23d7d5740c7958a644fb90ef0cba19ca39bd2c6534fb670b
T07 Target Wallet Receives 175 Million USDT
UTC 10-29 21:08:23 | Block 26300988 | Index 58 | Status 0x1
0xb6d7d3ffcbdd0465e1ab743a8d943218176cac7b15edefa7b7bcd5e853e4266f
T08 Target Wallet Receives 2 ETH
UTC 10-29 21:10:59 | Block 26301001 | Index 80 | Status 0x1
0xb9ecd720caf142fcd2c5eec36510930bc5d6a0c0ebfd69ec8084b47a464d2ae9
T09 GasStation Recharge
UTC 10-29 21:12:59 | Block 26301011 | Index 85 | Status 0x1
0x9a3a5d8ce9ae4d5865f21f92b741cc51fa75ac19cd9bb79d23fa2224ba38ccc3
T16 / T18 belong to third-party zero-value or dust memo clues, and are not deemed to participate in the attack due to transfers to the target address. Blocks and receipts can verify the existence of transactions; external address labels and natural person affiliations require additional evidence.
T10 USDT Unlimited Authorization
UTC 10-29 21:12:59 | Block 26301011 | Index 86 | Status 0x1
0x3825815ffa7d04c818f11d6708da7c87f6dc218362a501f432b7f26a651739c6
T11 USDT Payment Fees
UTC 10-29 21:12:59 | Block 26301011 | Index 87 | Status 0x1
0x11be88b460501b4652e760c41e08cc1f18575e14b6c6ffbb3383e043c2decf34
T12 Second USDT Authorization
UTC 10-29 21:14:35 | Block 26301019 | Index 70 | Status 0x1
0x4c96890a51f65f5ce41f6b2921b43fd5c62a467eba87de2f29fc32c75f7bfbc8
T13 USDT Blacklist Transaction
UTC 10-29 21:14:59 | Block 26301021 | Index 199 | Status 0x1
0x0c07a5e428ce233a3bcb40f257ad899594421341d63ce94016822063362707bf
T14 Target Wallet Receives 20 ETH
UTC 10-29 21:29:11 | Block 26301092 | Index 58 | Status 0x1
0xbba4ede016d92774812b742656cb1b7ee50fa6ca31315f5d168707cccd72a4b7
T15 Target Wallet Transfers Out ETH
UTC 10-29 21:46:23 | Block 26301178 | Index 127 | Status 0x1
0xcb9f8b9fab72935389945f689f4b012b0005738108234daa6594d0f31469a39f
T16 Third-Party Zero-Value Memo Transaction
UTC 10-29 22:06:47 | Block 26301280 | Index 300 | Status 0x1
0x5594c9508b7ec5fc5b1dca0892acf554c89f595cd14e3237dd197823870360ed
T17 Revoke EIP-7702 Delegation
UTC 10-30 00:10:35 | Block 26301896 | Index 190 | Status 0x1
0xafbf94c92a8d749988411669fa14d4f8866d9b4420b4ebd299f28e958dac7209
T18 Third-Party 69wei Memo Transaction
UTC 10-30 02:52:11 | Block 26302699 | Index 138 | Status 0x1
0xf117e2f197fdf502cad7194ed362f2551d2df4032c858fdd3ca5f6f758bbf34e
T19 Newly Added: 0.000100 USDT Micro Transfer
UTC 10-30 04:52:23 | Block 26303299 | Index 255 | Status 0x1
0x2b482d64b3a8a8b63db8d3634662cd9145b95fb87f8d7633c6d1bc41bf767e88
T19 has obtained transaction, receipt, and Transfer logs; not counted in the original 18 hashes / outer signature verification total.
T16 / T18 belong to third-party zero-value or dust memo clues, and are not deemed to participate in the attack due to transfers to the target address. Blocks and receipts can verify the existence of transactions; external address labels and natural person affiliations require additional evidence.
Verifiable Source Registration (One)
Source numbers correspond to the main text; clicking the link under the title can open the original page.
[S01] Binance | Security Incident Update
https://www.binance.com/en/support/announcement/detail/c5a8729a97ac486d963784d96c5642d7
Page 2026-10-30 02:23, time zone not marked; the full text was read through search indexing this time. Official preliminary investigation, total amount, suspension, and commitment.
[S02] TRM Labs | Binance incident analysis
https://www.trmlabs.com/resources/blog/north-korea-steals-usd-6-36-billion-from-binance-in-the-largest-hack-in-history
Page 2026-10-29; text statistics as of 10-30 00:30 UTC. Institutional cross-chain scale and attribution, read through search indexing.
[S03] Reuters / MarketScreener | Analysts react
https://www.marketscreener.com/news/analysts-react-as-binance-freezes-assets-after-6-3-billion-security-breach-ce785fdad08cf127
Page 10-29 23:40 EDT; cited Chainalysis 00:30 UTC statistics. Media citation, not impersonating the original ledger.
[S04] LlamaRisk / Aave governance | Response
https://governance.aave.com/t/binance-hot-wallet-exploit-aaves-response/25954
Last updated 2026-10-30 01:00 UTC. First-party risk service provider discloses lending and freezing measures.
[S05] Reuters / Investing.com | Issuer freezes
https://www.investing.com/news/stock-market-news/tether-circle-freeze-238-billion-after-binance-reports-security-incident-4985511
10-29 18:26, updated 18:30, page timezone unclear. Earlier media snapshot of the issuer's freeze.
[S06] Reuters / AsiaOne | Binance security incident
https://www.asiaone.com/money/binance-hacked-32b-assets-frozen-security-incident
Page 10-30 01:47, timezone unclear. Cited from Alpha, WLFI / BitGo; new currency in the title cannot be mixed with USD in the text.
[S07] CoinMarketCal / TradingView | Arbitrum freezes
https://www.tradingview.com/news/coinmarketcal%3A90e434733094b%3A0-arbitrum-security-council-freezes-funds-linked-to-binance-exploit-30-oct-2026/
2026-10-30; cited Arbitrum statement. Original X full text not directly verified.
Verifiable Sources and Evidence Attachments
All materials are compiled as of the report's cutoff time; different sources cover inconsistent timeframes.
[S08] Ethereum EIP-7702 | Set Code for EOAs
https://eips.ethereum.org/EIPS/eip-7702
Source of protocol rules; authorization summary, nonce, zero address clearance, and processing order.
[S09] MetaMask | Gas Station
https://support.metamask.io/manage-crypto/transactions/metamask-gas-station/
Official feature description; can actively choose other tokens to pay fees, does not prove specific client or server logs for this case.
[S10] Binance TH | Deposit / withdrawal notice
https://www.binance.th/en/announcement/crypto-deposit-%7C-withdrawal/d596e0d30341443aa477056a126e712a
2026-10-30; regional entity public statement. Retrieved through search index, does not replace current service status check.
[S11] Cointelegraph | Live incident coverage
https://cointelegraph.com/news/binance-linked-wallet-faces-possible-exploit-blockchain-researcher-warns
Latest readable entry obtained 10-30 03:49 UTC; used for cross-checking progress and finding original post entry.
[S12] Reuters / The Star | TRM attribution
https://www.thestar.com.my/tech/tech-news/2026/10/30/blockchain-analysis-firm-trm-says-north-korea-behind-binance-crypto-theft
2026-10-30 12:33 MYT (13:33 JST); used to verify attribution study's dissemination and timing on the same day.
Local Materials and Evidence Package
[O01] User-provided GCSABinanceForensicReportCN.pdf, 10 pages, version 1.0. Its old CSV, HTML, and scripts were not provided with the document, and this does not impersonate received attachments.
Original PDF SHA-256: 9cd681ed994fa6d757e7caf0d492407d8910bc973ce441aa7f1d7af42741994e
[E01] This evidence package: original 18 transactions and newly added T19's public RPC transactions / receipts, designated block queries, signature verification results, failure responses, source registration, and SHA256SUMS.txt. Provider: ethereum-rpc.publicnode.com / ethereum.publicnode.com; both domains belong to the same service provider.
Attachments only contain materials actually obtained and generated this time. Hashes are used to check file changes, not judicial timestamps, and cannot prove upstream nodes or media content are necessarily correct. No internal account 5 households, keys, private IPs, or unobtained logs are attached.
 Risk warning
 Risk warning

Popular articles





